Prohibited License Policy Enforcement in CI Pipelines
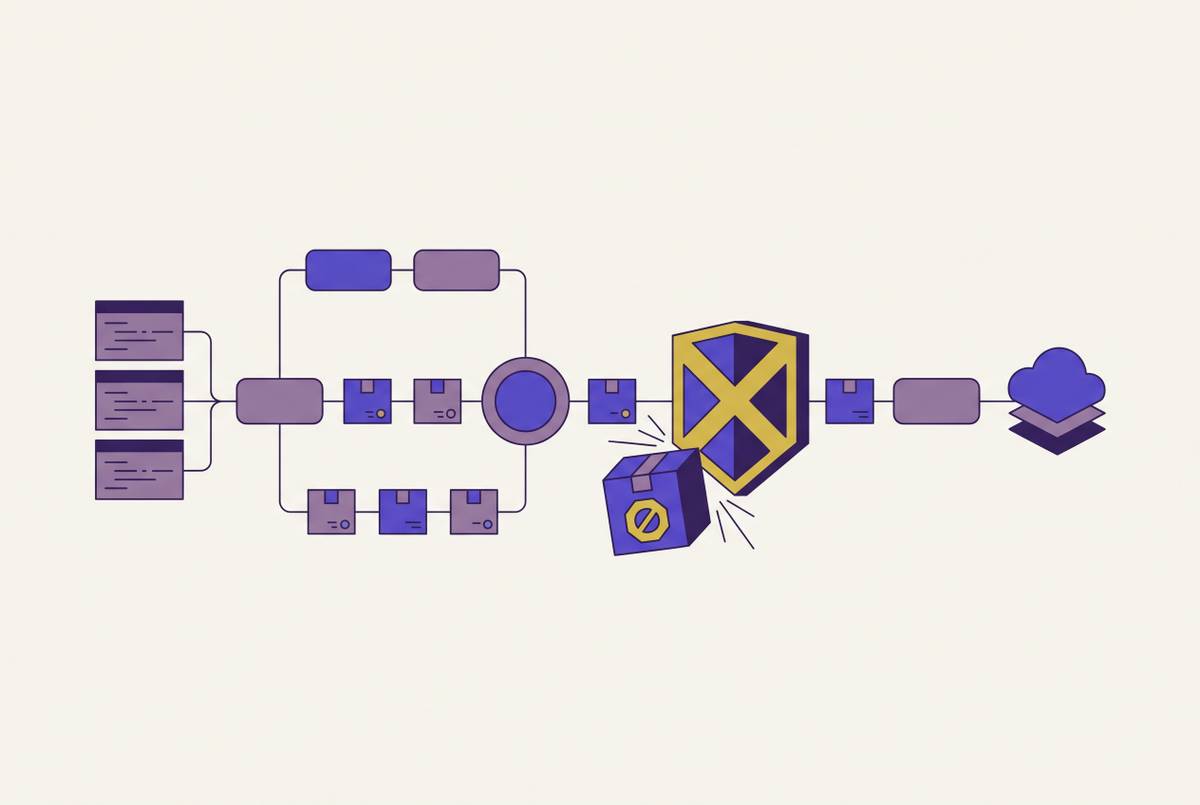
Scan resolved dependencies against policy rules before code reaches production.
Renata Osei-Bonsu
12 stories
Scan resolved dependencies against policy rules before code reaches production.
Engineering teams must now prove payment-system controls work continuously, not just before audits.
Distributions now enforce reproducible builds to verify binaries match their source code.
NIST now names reproducible builds and coded toolchains as core security controls.
Validate vendor SBOMs before a breach forces you to rely on incomplete paperwork.
Regulated industries face four compounding open source risks that point-in-time scans cannot catch.
Transparency logs provide the tamper-proof audit trails compliance frameworks now demand.
SLSA levels provide a roadmap for building supply chain security without reinventing your pipeline.
Organizations must document vulnerability detection, prioritization.
Federal buyers now enforce SBOMs through fragmented regulations, not unified standards.
Continuous generation ties SBOMs to actual deployments, while snapshots lag behind as systems drift.
Static policies fail because software dependencies never stop changing.