Third-Party Component Provenance in Software Acquisition Due Diligence
Verified component provenance is now the valuation lever in software M&A.
Provenance for third-party components is not a post-deal audit item any longer. In the 2026 software acquisition market, it is the diligence signal that separates a defensible valuation from an inherited liability. Acquirers who demand verifiable provenance before closing surface compounding vulnerability risk, hidden dependency debt, and supply chain exposure while they still retain negotiating leverage.
Why third-party components have become the dominant liability in software acquisitions
An acquirer purchasing a software company is not buying a product. The engineering team owns a thin layer of original code wrapped around a substantial volume of other people's work. That composition makes third-party components the largest attack surface in any acquired system, and the one the target's own team has the least direct control over.
The risk is not merely significant. An acquirer walking into a deal armed with last year's risk assumptions is walking in with stale data. The gap between discovery and fix represents a window of exposure that transfers silently with the asset.
License exposure compounds the security exposure. A provenance gap that surfaces as a security concern can quickly become a transaction risk with legal and financial dimensions. The liabilities an acquirer assumes are not abstract. They are enumerable, and they belong in the valuation model.
How supply chain attacks reach acquired software before due diligence begins
The attack surface spans the entire delivery chain. Dependency resolution at development time, build and CI/CD infrastructure, and distribution through package registries each constitute a distinct and independently exploitable entry point. A compromise at any one of these stages reaches the software an acquirer is evaluating, often without leaving a trace visible in a document review.
Attackers no longer sit at a keyboard and wait. They automate and self-replicate. Pulling a compromised package does not end the compromise. Credentials stolen during installation remain valid, so remediation requires rotating tokens and auditing CI/CD runners, not just bumping a version number.
Manifest-based scanning misses a significant fraction of real-world component ingestion. A meaningful share of open-source components enter codebases outside standard package managers, as copy-pasted snippets, direct vendor inclusions, or AI-generated code. An acquirer relying on a dependency manifest is examining a partial inventory while believing it is complete.
Environment drift operates by the same mechanism. The software that was tested is not necessarily the software that shipped. This gap sits outside the dependency graph entirely, in the infrastructure that assembles it.
What the 2026 regulatory environment now requires acquirers to prove
The baseline for acceptable provenance evidence has been formally raised by multiple converging regulatory instruments. Acquirers who plan around the old baseline are planning around superseded requirements. What used to count as reasonable care no longer does.
The 2026 Minimum Elements for an SBOM, published by CISA, NSA, FBI, and fifteen international partners, replaces the 2021 NTIA baseline and expands to 17 fields. Manufacturers selling products with digital elements in the EU market must maintain SBOMs covering at least direct dependencies in a commonly used, machine-readable format, available to market surveillance authorities on request. The CRA does not require publication or provision to customers, but the maintenance obligation is absolute.
An AI Bill of Materials is becoming a parallel requirement. The G7 Cybersecurity Working Group, including CISA, BSI, ANSSI, NCSC, ACN, CSE, NCO, and the EU Commission, published Software Bill of Materials for AI: Minimum Elements on May 12, 2026. Models now influence application behavior as much as source code, and a traditional SBOM does not capture that risk.
The practical implication for acquirers is straightforward. If a target's SBOM does not satisfy the 2026 Minimum Elements, or if its AI components lack an AI BOM, it carries a compliance gap that will require remediation post-close. It is not a post-close operational expense. It is a purchase price adjustment waiting to be identified.
Why a detailed SBOM is not the same as verified provenance
A large, detailed-looking SBOM can create false confidence. Quantity is not security quality. A thorough inventory of what was present at one moment tells an acquirer very little about what is running now. The structural limitation of any SBOM is temporal. An SBOM generated before the compromise would accurately reflect the legitimate state of the project while missing the fact that the project had been quietly captured.
Container-layer blind spots compound the gap. The 2026 standard for containerized software requires SBOMs that cover all container contents as a top-level manifest, not just the application payload. A target that produces an application SBOM without container-layer coverage is presenting a partial inventory as a complete one.
The SBOM-as-compliance objection has a name. The dominant critique is that enterprise security has turned SBOMs into governance theatre, a document that proves an organization looked, not one that proves anything was prevented or is currently enforced. The answer to that objection is not to abandon SBOMs. Cryptographic attestations, signed build provenance, and input-derived hashes make tampering detectable and policy-enforceable. The document becomes evidence rather than decoration.
The evidence standard that separates verified provenance from paper compliance
Verified provenance means a chain of cryptographically signed, reproducible evidence that an artifact came from an expected source, was built by an expected process, and has not been tampered with since. Documentation alone does not satisfy this definition. A claim that a build was secure is not the same as proof that the build was what it purported to be.
SLSA, or Supply chain Levels for Software Artifacts, gives you a mature, graduated framework for assessing build provenance claims. SLSA Build Level 3 with Sigstore/Cosign-verifiable attestations represents a high but achievable standard. The framework gives acquirers a language for evaluating exactly how much evidence a target can produce about where its artifacts came from.
Input-derived hashes are the mechanism that makes provenance actionable at deal time and post-close. Acquirers can attach those hashes to specific deployment versions and, when a CVE surfaces post-close, determine rapidly which deployed versions are affected without grepping logs or rescanning images. Hash-level blocking or patching becomes possible. You can target exactly the affected versions instead of mounting a broad response across the fleet.
Binary analysis fills the gap where source code or vendor-provided SBOMs are unavailable. Acquirers can inspect compiled executables, firmware, and container images across multiple architectures without source code. So they verify the software they actually received instead of relying on vendor documentation. The capability is particularly valuable for M&A due diligence where source code access is contractually restricted. An acquirer who cannot see the source can still inspect the artifact.
Generation Context, now required by the 2026 Minimum Elements, lets an acquirer immediately assess the trust level of any SBOM they receive. A document generated from source during an active build is materially more trustworthy than one reconstructed from a shipped binary after the fact. The field encodes the difference between evidence produced at the moment of creation and a retrospective reconstruction.
How to structure a provenance-first due diligence review before deal close
The organizing principle is that provenance review must happen before deal close, not after. A flaw identified during diligence is a price adjustment. A flaw identified after closing is an expense.
You begin with the SBOM demand letter, evaluated against the 2026 Minimum Elements. The immediate questions are whether the SBOM covers transitive dependencies to full depth or only direct dependencies, and what Generation Context is declared: source, build, or binary analysis. A silently absent field is a red flag. The absence of one is a compliance gap, not an acceptable omission.
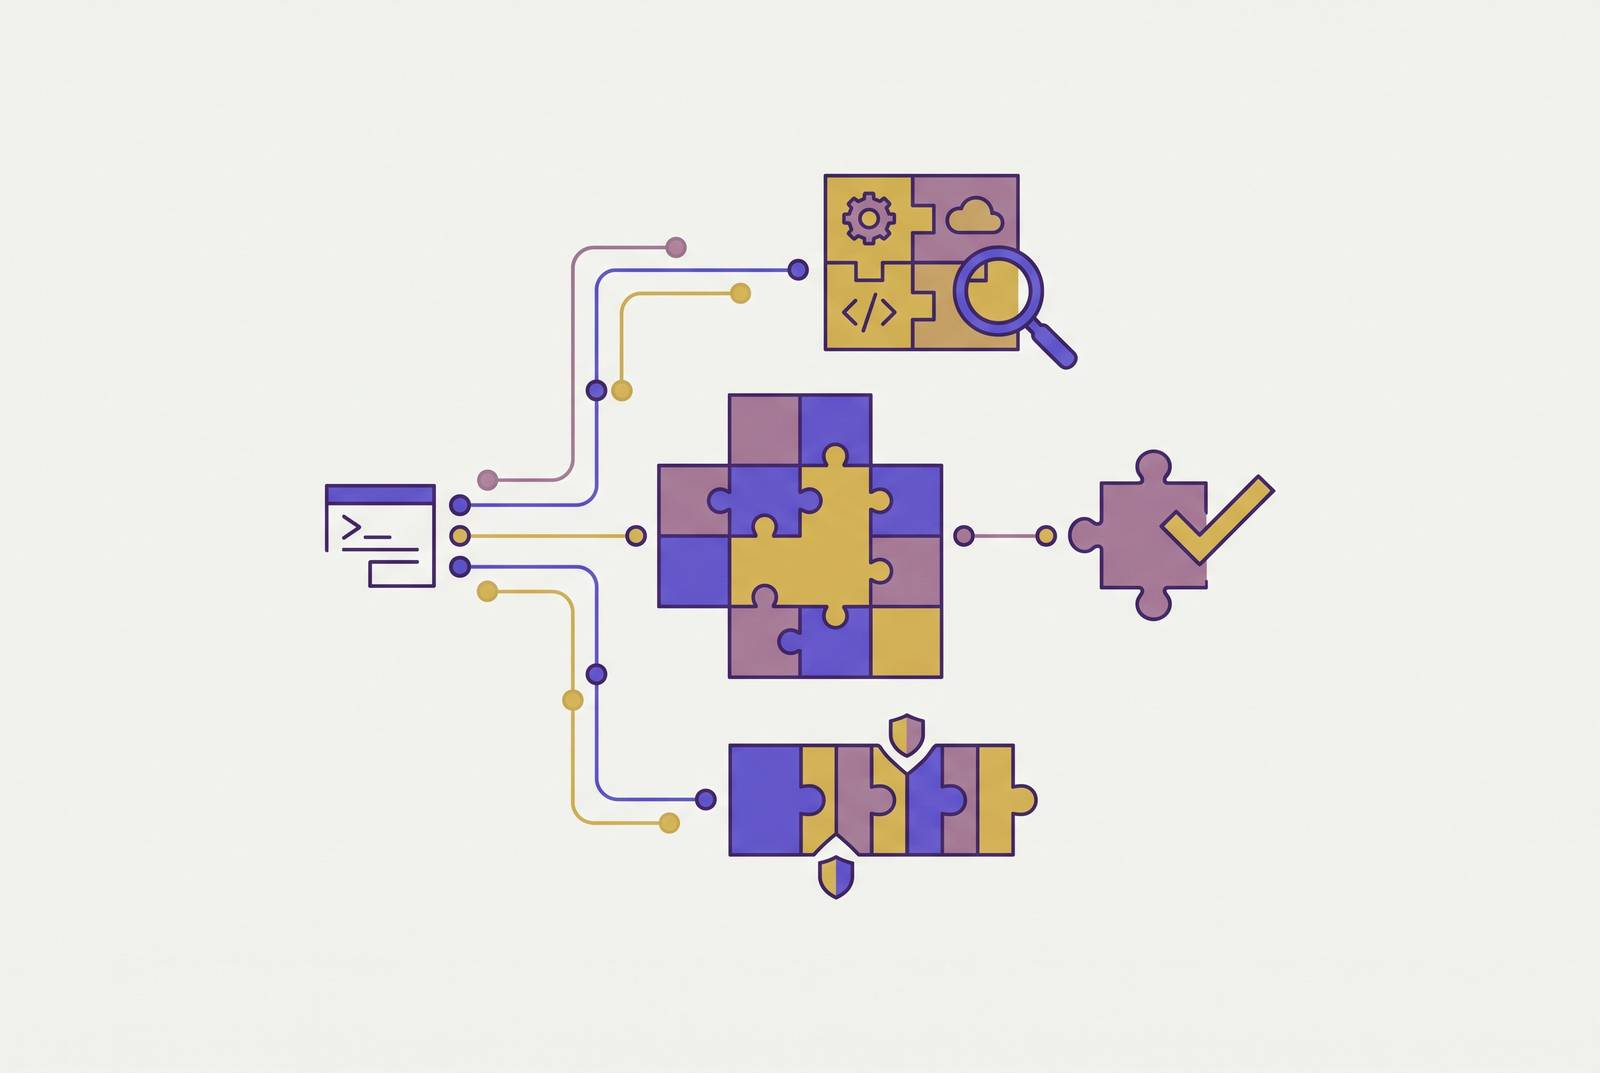
Cross-referencing the SBOM against independent binary analysis is the next step, particularly for components delivered as compiled artifacts, firmware, or container images. Independent inspection of the actual artifact catches what the document omits. NIST SP 1326's five due diligence categories provide a structured checklist. Foreign ownership and control asks who owns the target's dependencies and where their maintainers are geographically located. Provenance asks whether the target can produce signed build provenance for its artifacts, and at what SLSA level. Resilience asks how quickly the target identifies and remediates CVEs in its dependency graph, where long remediation windows signal accumulated security debt. Foundational cyber practices asks whether builds are ephemeral and isolated, whether commits are signed, and whether least privilege is enforced in CI/CD. Supply chain tiers asks whether the target has evaluated its own suppliers and sub-tier dependencies, or only its direct dependency list.
Environment reproducibility functions as a provenance signal in its own right. A target whose build environments are pinned, declaratively defined, and hash-verified provides a stronger provenance guarantee than one relying on mutable base images or undeclared transitive toolchain dependencies. The CVE response workflow is the final assessment. It is how rapidly the target can identify which deployed versions are affected and execute a targeted patch. A target with input-derived hashes on its deployments can answer this question in minutes. One without them cannot answer it reliably at all.
What accumulated dependency debt looks like when it surfaces post-close, and how to price it
Security debt from third-party components compounds differently from technical debt in first-party code. They must wait for a patch from a maintainer who may be unresponsive, then integrate and redeploy. The acquirer inherits an exposure window they did not create and cannot close on their own schedule.
The most severe, long-lived vulnerabilities disproportionately originate in third-party code, according to Veracode's 2026 State of Software Security Report. The component of security debt that is hardest to retire is precisely the component an acquirer inherits from outside the target's control. License risk is a parallel debt vector. The options are negotiating licenses at an unknown cost, rewriting the affected functionality at an engineering cost, or removing the feature at a product cost. All three are expensive, and none were priced into the original transaction.
A supply-chain compromise in the target's dependency graph has a remediation tail beyond version bumps. Any credentials harvested from the target's CI/CD environment during an active infection remain valid until rotated. None of that work is visible in an SBOM review alone. An acquirer who reviewed the SBOM and declared due diligence complete has missed the most expensive part of the cleanup.
The pricing framework translates these findings into deal terms. Each provenance gap maps to one of three cost categories. Compliance cost is what it takes to bring the SBOM and AI BOM to the 2026 standard required by the EU CRA or NIST SP 1326. Each belongs in the valuation model before the deal closes.
Why deterministic environments are the infrastructure foundation that makes provenance claims trustworthy
An SBOM and a signed attestation are only as trustworthy as the build environment that produced them. If the environment is mutable, unversioned, or undeclared, the provenance chain has a gap at its foundation that no downstream signing step can close. A signature over an artifact built in an unknown environment proves only that someone signed something.
To apply Zero Trust to software delivery, you must verify every critical step in the SDLC, including the build environment itself. The Cloud Security Alliance makes the case explicitly in its 2026 Zero Trust and supply chain guidance. An environment that is not pinned and verified is one where trust is assumed rather than earned. A build pipeline whose environment components are not locked to verified versions can silently diverge from what was audited, producing artifacts whose provenance cannot be fully vouched for even if the application dependencies are pinned.
The declarative environment manifest is what makes reproducibility auditable. It is a human-readable, version-controlled definition of every tool, library, and environment variable in the build. Input-derived hashes on environments close the last gap. When the environment itself is hashed alongside the application inputs, an acquirer can verify not just what packages were declared but that the declared environment was actually what ran. Rapid CVE discovery and hash-level blocking or patching become possible without rescanning every image individually.
Deterministic environments also resolve the SBOM generation timing problem. When an environment is fully declared and reproducible, an SBOM can be generated at any point and will accurately reflect what built the artifact. The provenance evidence is a natural byproduct of the build process, not an after-the-fact reconstruction.
For acquirers, the practical question to add to due diligence is whether the target can reproduce any prior release from a declared, hash-verified environment. A yes with evidence is a provenance chain. The answer to that single question reveals more about the target's supply chain hygiene than a thousand-line SBOM ever could.